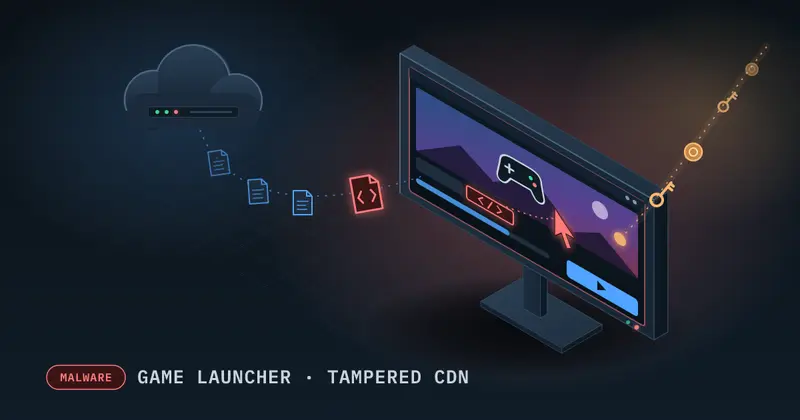
The PC launcher of the popular game Goddess of Victory: NIKKE was used to deliver malware, according to a technical report published on GitHub on 3 November by a researcher using the name MotherSphere. Four JavaScript files that the launcher loads from publisher Level Infinite's official CDN were modified on 27 September 2026 so that they pulled in an outside script. The earliest reported start of the remote-access agent on a player's PC was 23 October (Inven Global says 24 October at the latest), and the payload ran only on some launches.
What the agent can do, per the report: while the launcher is open, the operator can run any command, read and download files and take screenshots. It targets the NIKKE login saved by the launcher, passwords and cookies saved in Chrome, Edge, Brave, Vivaldi, Opera and Firefox, SSH keys, cloud, developer and AI-tool tokens, PuTTY and WinSCP sessions, and data from 28 crypto-wallet extensions. On Windows it registers a DLL so that Chrome keeps loading it after the launcher closes. Players on Linux and Steam Deck through Proton are also exposed. What was actually taken from each PC is not confirmed.
Fix: one file was cleaned at the origin on 28 October, but some CDN servers kept serving the old copy; the other three were replaced on 3 November (17:04–17:23 GMT) and the last stale copies on 4 November. The official NIKKE account on X said the launcher's script files appear to have been tampered with by a third party, that client fixes and an update are in place, and that more details will follow. Inven Global notes that players on Taiwan's Bahamut forum said some Japanese-server players found the same traces in their logs.
Still unknown: how the attacker got write access to Level Infinite's CDN, how many players were infected, and whether other Level Infinite games were touched. Replacing the files stops new infections but does not clean PCs that were already infected. The analysis covers the PC launcher only, not the mobile game.